

 1933 Kundenrezensionen
Die CIPM Prüfung auf die geeigneteste Weise vorbereiten
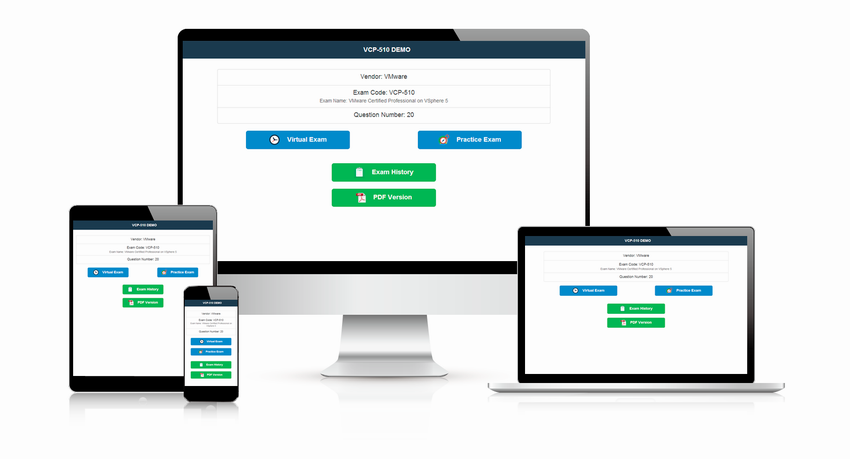
Jeder hat seine eigene Bevorzugung für die Prüfungsvorbereitung. Auf die geeigneteste Weise kann man sich am besten auf CIPM Prüfung vorbereiten. Das Technikteam von ZertFragen bietet insgesamt 3 Versionen von CIPM Prüfung, nämlich PDF, Online Test Engine sowie simulierte Prüfungssoftware. Alle drei Versionen enthalten die gleichen Zertifizierungsfragen der CIPM (Certified Information Privacy Manager (CIPM)), aber in unterschiedlicher Form. Deshalb hat jede Version ihre eigene Überlegenheit, z.B. mit PDF Version können Sie ohne Internet noch die Zertifizierungsfragen der CIPM lernen. Mit dem Simulationssoftware sind Sie in der Lage, die Prüfungsatmosphäre im voraus zu erleben. Dadurch wir Ihre Angst vor CIPM Prüfung weniger sein!
Um die geeigneteste Version auszuwählen, empfehlen wir, dass Sie vor dem Kauf die Demo von drei Versionen zur CIPM Prüfung probeweise zu gebrauchen. Demo ist natürlich kostenlos. Sie können sie auf unserer Webseite gratis herunterladen. Nach dem Kauf bieten wir noch einjährige Aktualisierungsdienst zur CIPM Zertifizierungsfragen. Sie können sie ganz unbesorgt benutzen. Wir glauben, mit der geeignetesten Version können Sie sich am besten auf die CIPM Prüfung vorbereiten.
Wir wünschen Ihnen herzlich, dass Sie mit Hilfe unserer Produkte das CIPM Zertifikat zügig erwerben und ein besseres Leben in der Zukunft führen können. Irgendwann Sie Fragen über CIPM Prüfung haben, können Sie mit uns online kontaktieren oder E-mail schicken!
Einfach und bequem zu kaufen: Um Ihren Kauf abzuschließen, gibt es zuvor nur ein paar Schritte. Nachdem Sie unser Produkt per E-mail empfangen, herunterladen Sie die Anhänge darin, danach beginnen Sie, fleißig und konzentriert zu lernen!
IAPP CIPM Prüfungsplan:
| Thema | Einzelheiten |
|---|---|
| Thema 1 |
|
| Thema 2 |
|
| Thema 3 |
|
| Thema 4 |
|
Referenz: https://iapp.org/certify/get-certified/cipm/
Schnell die CIPM bestehen ohne Geldverschwendung
Wegen der Verlässlichkeit unserer Produkte haben schon zahlreiche Benutzer die CIPM zügig bestanden. Laut Statistiken dürfen Sie sich nach konzentriertem Gebruach innerhalb nur 20 bis 30 Stunden auf CIPM sehr gut vorbereiten. Viele Prüfungsteilnehmer haben schon ins Arbeitsleben eingestiegen. Die Freizeit ist sehr wenig, deswegen bieten wir die effizienten Zertifizierungsfragen, mit denen Sie die CIPM Prüfung innerhalb einer kurzen Zeit bestehen können.
Weil die Pass-Rate sehr hoch ist, können wir Ihnen garantieren, falls Sie die CIPM Zertifizierungsprüfung nicht schaffen, erstatten wir alle Ihre bezahlten Kosten. Sie brauchen nur, uns das Zeugnis per E-mail zu schichen. Wir tun unser Bestes, um Ihren finanziellen Verlust am möglichsten zu vermindern. Wir ZertFragen ist kundenorientiert und vertrauenswürdig!
Beste Zertifizierungsfragen der IAPP CIPM mit günstigem Preis
Durch langjärige Erforschungen und Bemühungen haben IT-Experten aus ZertFrafen die anspruchvollen Zertifizierungsfragen für CIPM gefertigt. Die zuverlässigen Zertifizierungsfragen enthalten echte Fragen aud den früheren CIPM Prüfungen. Fast jede Antworte der Prüfungsaufgaben hat ausführliche Erläuterungen, mit denen Sie die Fachkenntnisse der CIPM Prüfung gut beherrschen können.

Die Zertifizierungsfragen der IAPP CIPM (Certified Information Privacy Manager (CIPM)) von hoher Qualität kosten Sie nicht viel. Der Preis ist im Vergleich zu anderen Lieferanten sehr günstig. Außerdem bieten wir ab und zu Rabatte auf bestimmte Produkte. Deshalb können Sie sich uns vor dem Bezahlen der CIPM Zertifizierungsfragen online erkundigen, ob es zu jener Zeit einen Rabatt-Code für die CIPM Prüfung gibt.
Sie können sowohl online mit Kreditkarte zahlen oder direkt auf unser Konto überweisen. Ihre persönlichen Informationen werden von uns gut bewahrt, darum brauchen Sie keine Sorge zu machen. Nach dem Bezahlen werden Sie die Zertifizierungsfragen der CIPM sofort per E-mail erhalten.
IAPP Certified Information Privacy Manager (CIPM) CIPM Prüfungsfragen mit Lösungen
SCENARIO
Please use the following to answer the next QUESTION:
Natalia, CFO of the Nationwide Grill restaurant chain, had never seen her fellow executives so anxious. Last week, a data processing firm used by the company reported that its system may have been hacked, and customer data such as names, addresses, and birthdays may have been compromised. Although the attempt was proven unsuccessful, the scare has prompted several Nationwide Grill executives to Question the company's privacy program at today's meeting.
Alice, a vice president, said that the incident could have opened the door to lawsuits, potentially damaging Nationwide Grill's market position. The Chief Information Officer (CIO), Brendan, tried to assure her that even if there had been an actual breach, the chances of a successful suit against the company were slim. But Alice remained unconvinced.
Spencer - a former CEO and currently a senior advisor - said that he had always warned against the use of contractors for data processing. At the very least, he argued, they should be held contractually liable for telling customers about any security incidents. In his view, Nationwide Grill should not be forced to soil the company name for a problem it did not cause.
One of the business development (BD) executives, Haley, then spoke, imploring everyone to see reason.
"Breaches can happen, despite organizations' best efforts," she remarked. "Reasonable preparedness is key." She reminded everyone of the incident seven years ago when the large grocery chain Tinkerton's had its financial information compromised after a large order of Nationwide Grill frozen dinners. As a long-time BD executive with a solid understanding of Tinkerton's's corporate culture, built up through many years of cultivating relationships, Haley was able to successfully manage the company's incident response.
Spencer replied that acting with reason means allowing security to be handled by the security functions within the company - not BD staff. In a similar way, he said, Human Resources (HR) needs to do a better job training employees to prevent incidents. He pointed out that Nationwide Grill employees are overwhelmed with posters, emails, and memos from both HR and the ethics department related to the company's privacy program. Both the volume and the duplication of information means that it is often ignored altogether.
Spencer said, "The company needs to dedicate itself to its privacy program and set regular in-person trainings for all staff once a month." Alice responded that the suggestion, while well-meaning, is not practical. With many locations, local HR departments need to have flexibility with their training schedules. Silently, Natalia agreed.
The senior advisor, Spencer, has a misconception regarding?
- A. The role of Human Resources employees in an organization's privacy program.
- B. The amount of responsibility that a data controller retains.
- C. The appropriate role of an organization's security department.
- D. The degree to which training can lessen the number of security incidents.
Antwort: B 🗳️
Erklärung: (Nur für ZertFragen-Mitglieder sichtbar)
What does it mean to "rationalize" data protection requirements?
- A. Address the less stringent laws and regulations, and inform stakeholders why they are applicable
- B. Determine where laws and regulations are redundant in order to eliminate some from requiring compliance
- C. Evaluate the costs and risks of applicable laws and regulations and address those that have the greatest penalties
- D. Look for overlaps in laws and regulations from which a common solution can be developed
Antwort: D 🗳️
Erklärung: (Nur für ZertFragen-Mitglieder sichtbar)
Under the General Data Protection Regulation (GDPR), what are the obligations of a processor that engages a sub-processor?
- A. The processor must Obtain the controllers specifiC written authorization and provide annual reports on the sub-processor'S performance.
- B. The processor must give the controller prior written notice and perform a preliminary audit of the sub- processor.
- C. The processor must receive a written agreement that the sub-processor will be fully liable to the controller for the performance of its obligations in relation to the personal data concerned.
- D. The processor must obtain the consent of the controller and ensure the sub-processor complies with data processing obligations that are equivalent to those that apply to the processor.
Antwort: D 🗳️
Erklärung: (Nur für ZertFragen-Mitglieder sichtbar)
(All of the following are the responsibilities of the privacy professional EXCEPT?)
- A. Defining the organization's data strategy.
- B. Monitoring compliance with data protection laws and regulations.
- C. Ensuring privacy audits are regularly conducted.
- D. Conducting privacy impact assessments (PIA).
Antwort: A 🗳️
Erklärung: (Nur für ZertFragen-Mitglieder sichtbar)
Last year Ecosoft 8150 was hacked and a number of servers and programs were affected. Since the incident, the company started collecting metrics on data privacy and system outages to try to stop it from happening in the future.
What analysis would be most helpful based on the data they have collected?
- A. Trend analysis.
- B. Business Resiliency.
- C. Compliance analysis.
- D. Return on Investment (ROI).
Antwort: A 🗳️
Seite 1 von 55 wird angezeigt.
Fragen 1-5 von 275 werden angezeigt.







Gaffky -
Ich bestand die CIPM Prüfung in der letzten Woche. Ich benutzte die Studienmaterialien von ZertFragen. Ihre Studienführung hilft mir, viel Zeit gespart zu haben. Ich lernte in nur 30 Stunden. Vielen Dank!